> For the complete documentation index, see [llms.txt](https://docs.keeper.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.keeper.io/keeper-connection-manager/authentication/account-approve-deny-workflow.md).
# Account Approve/Deny Workflow
Approve or Deny User's ability to authenticate with KSM using SSO
In an environment where KCM users may be automatically created from an SSO system, such as SAML or OpenID or PIV/CAC, administrators may wish to more tightly control whether those users are allows to use KCM. To facilitate this, KCM provides administrators an approve/deny workflow to decide whether an individual user should be allowed to authenticate with KCM using that SSO method.
## Configuring the KCM user creation workflow
To require approval for users signing in with a particular authentication method, use the `require-account-approval` property (or, for Docker, the `REQUIRE_ACCOUNT_APPROVAL` environment variable). This property accepts a comma-separated list of the names of all authentication methods that should require administrator approval. KCM supports the following authentication types:
Authentication Method
Name
Encrypted JSON
json
LDAP
ldap
OpenID
openid
SAML
saml
SSL/TLS Client Authentication (PIV/CAC)
ssl
For example, to require administrator approval for SAML and LDAP, you would specify:
```
require-account-approval: saml, ldap
```
The following examples shows a `docker.yaml` file with the SAML Authentication method enabled:
```yaml
guacamole:
image: keeper/guacamole:2
restart: unless-stopped
environment:
ACCEPT_EULA: "Y"
GUACD_HOSTNAME: "guacd"
SSL_PRIMARY_URI: "https://kcm.example.net"
SSL_CLIENT_AUTH_URI: "https://*.kcm.example.net"
SSL_SUBJECT_BASE_DN: "ou=test department,o=u.s. government,c=us"
POSTGRESQL_AUTO_CREATE_ACCOUNTS: "true"
REQUIRE_ACCOUNT_APPROVAL: "saml"
```
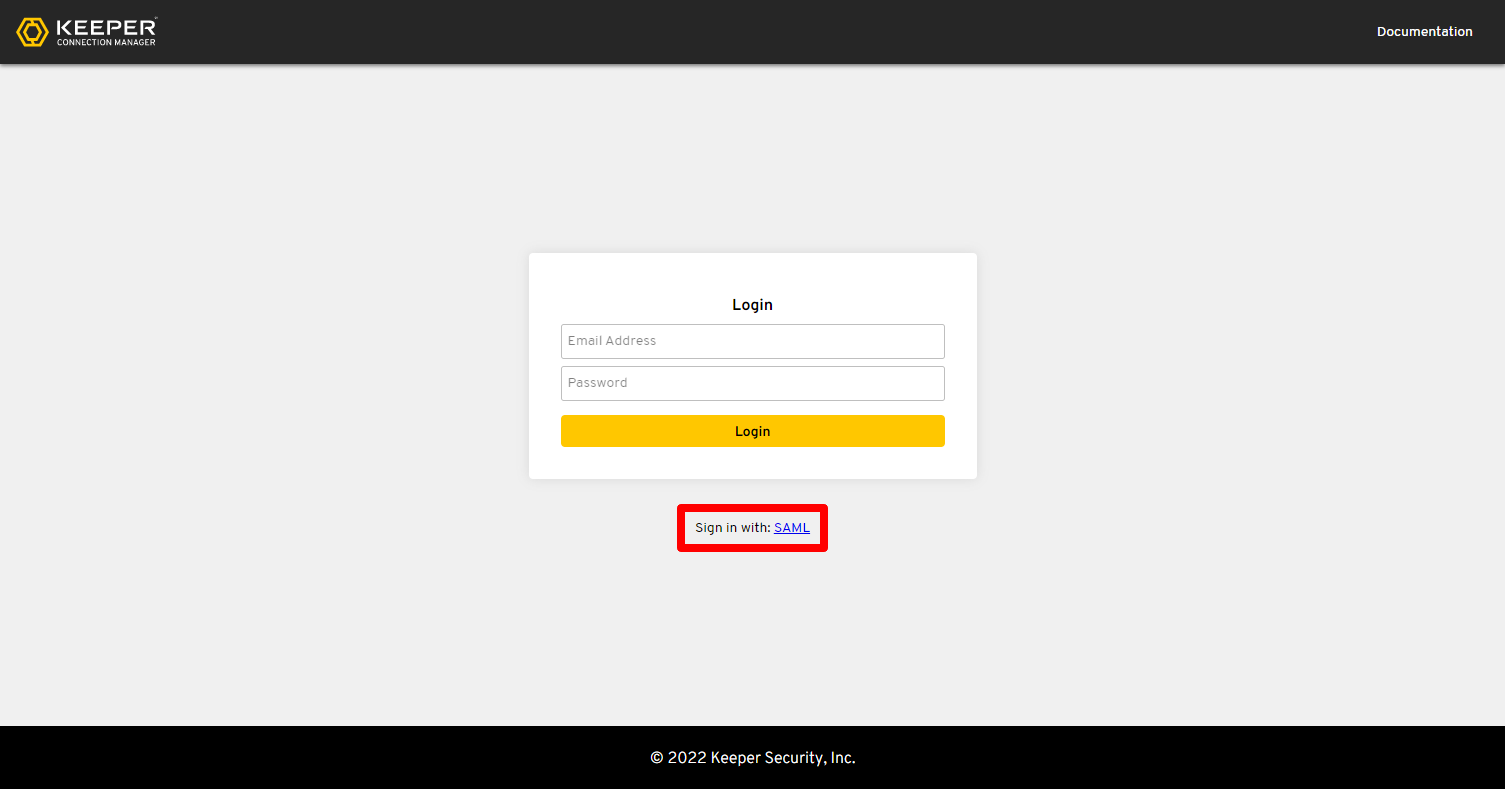
Once you have successfully configured and setup the authentication method, the corresponding SSO login method will be displayed on the login screen of the application. In the following image, the instance has been configured to use the `saml` authentication method:
Login Screen for SAML Authentication
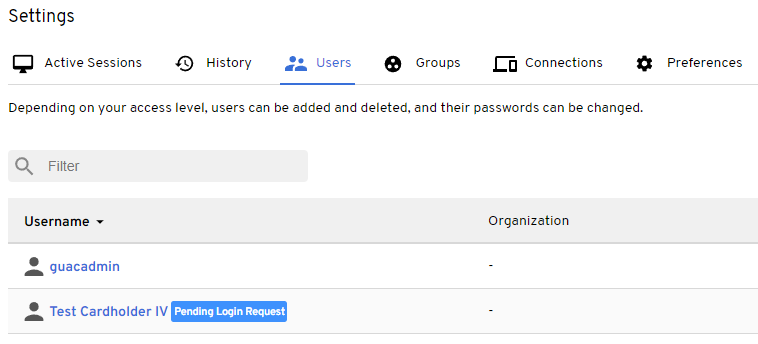
Users with at least one authentication method that needs to be approved or denied will be shown in the user list with a “Pending Login Request” badge next to their username:
Administrators can approve/deny access for that user via that authentication method by editing the user account in KCM:
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.keeper.io/keeper-connection-manager/authentication/account-approve-deny-workflow.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.